
Learn how to configure Auth0 as an identity provider for NocoDB.
This article briefs about the steps to configure Auth0 as Identity service provider for NocoDB
NocoDB, Retrieve SAML SSO Configuration details
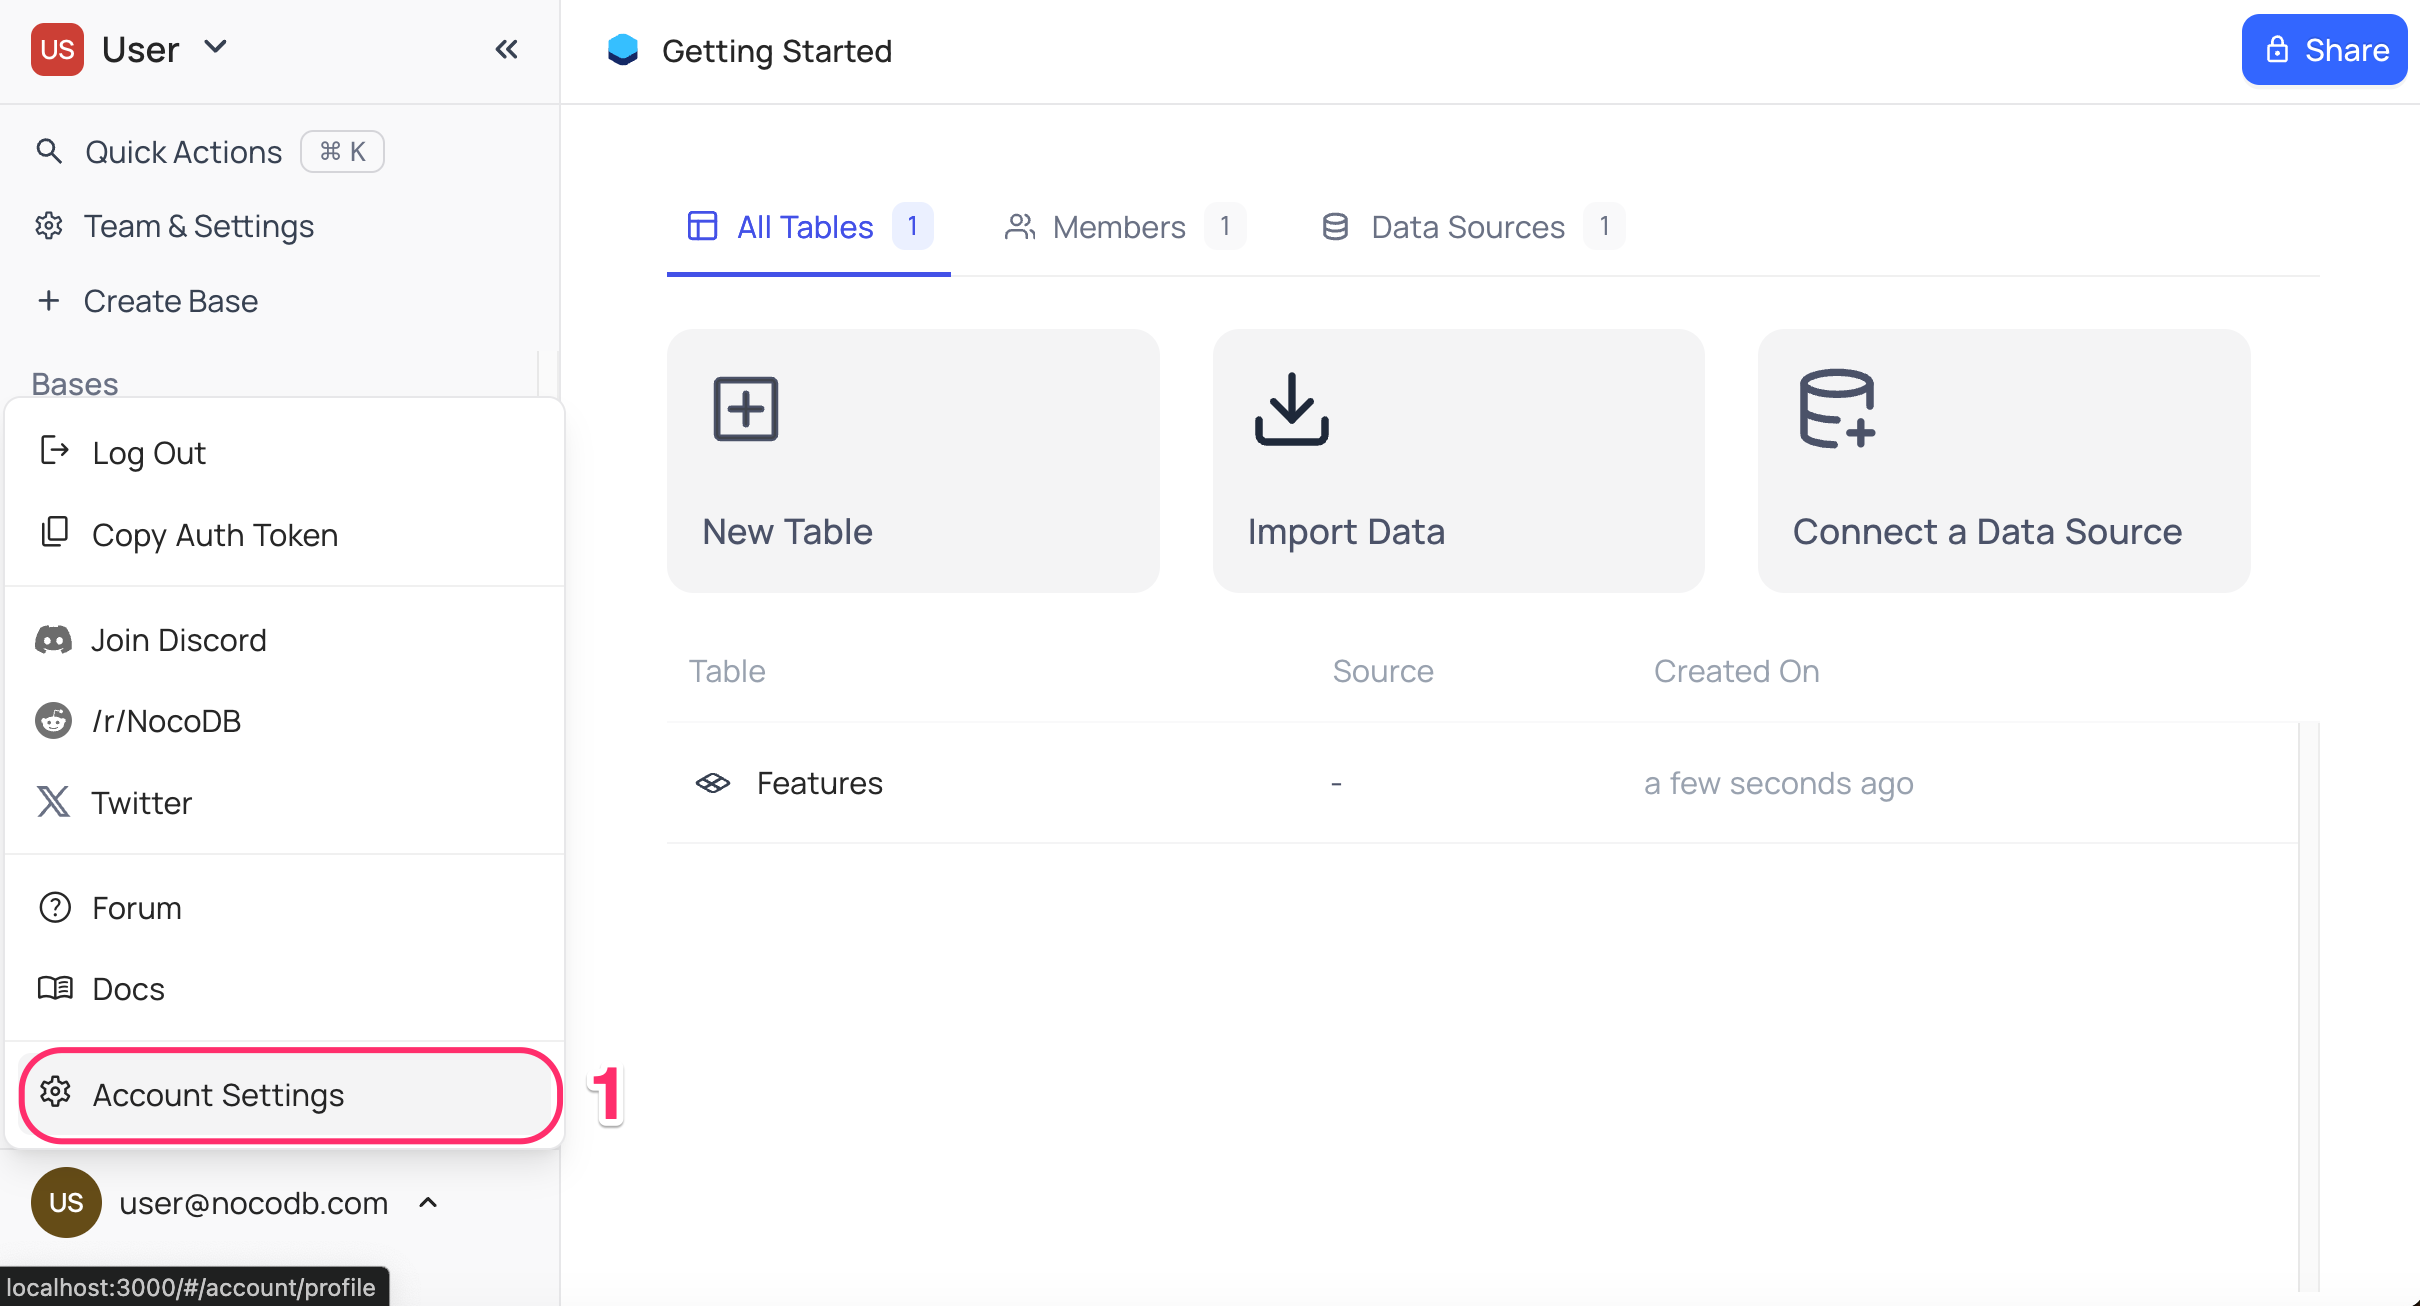
- Go to
Account Settings - Select
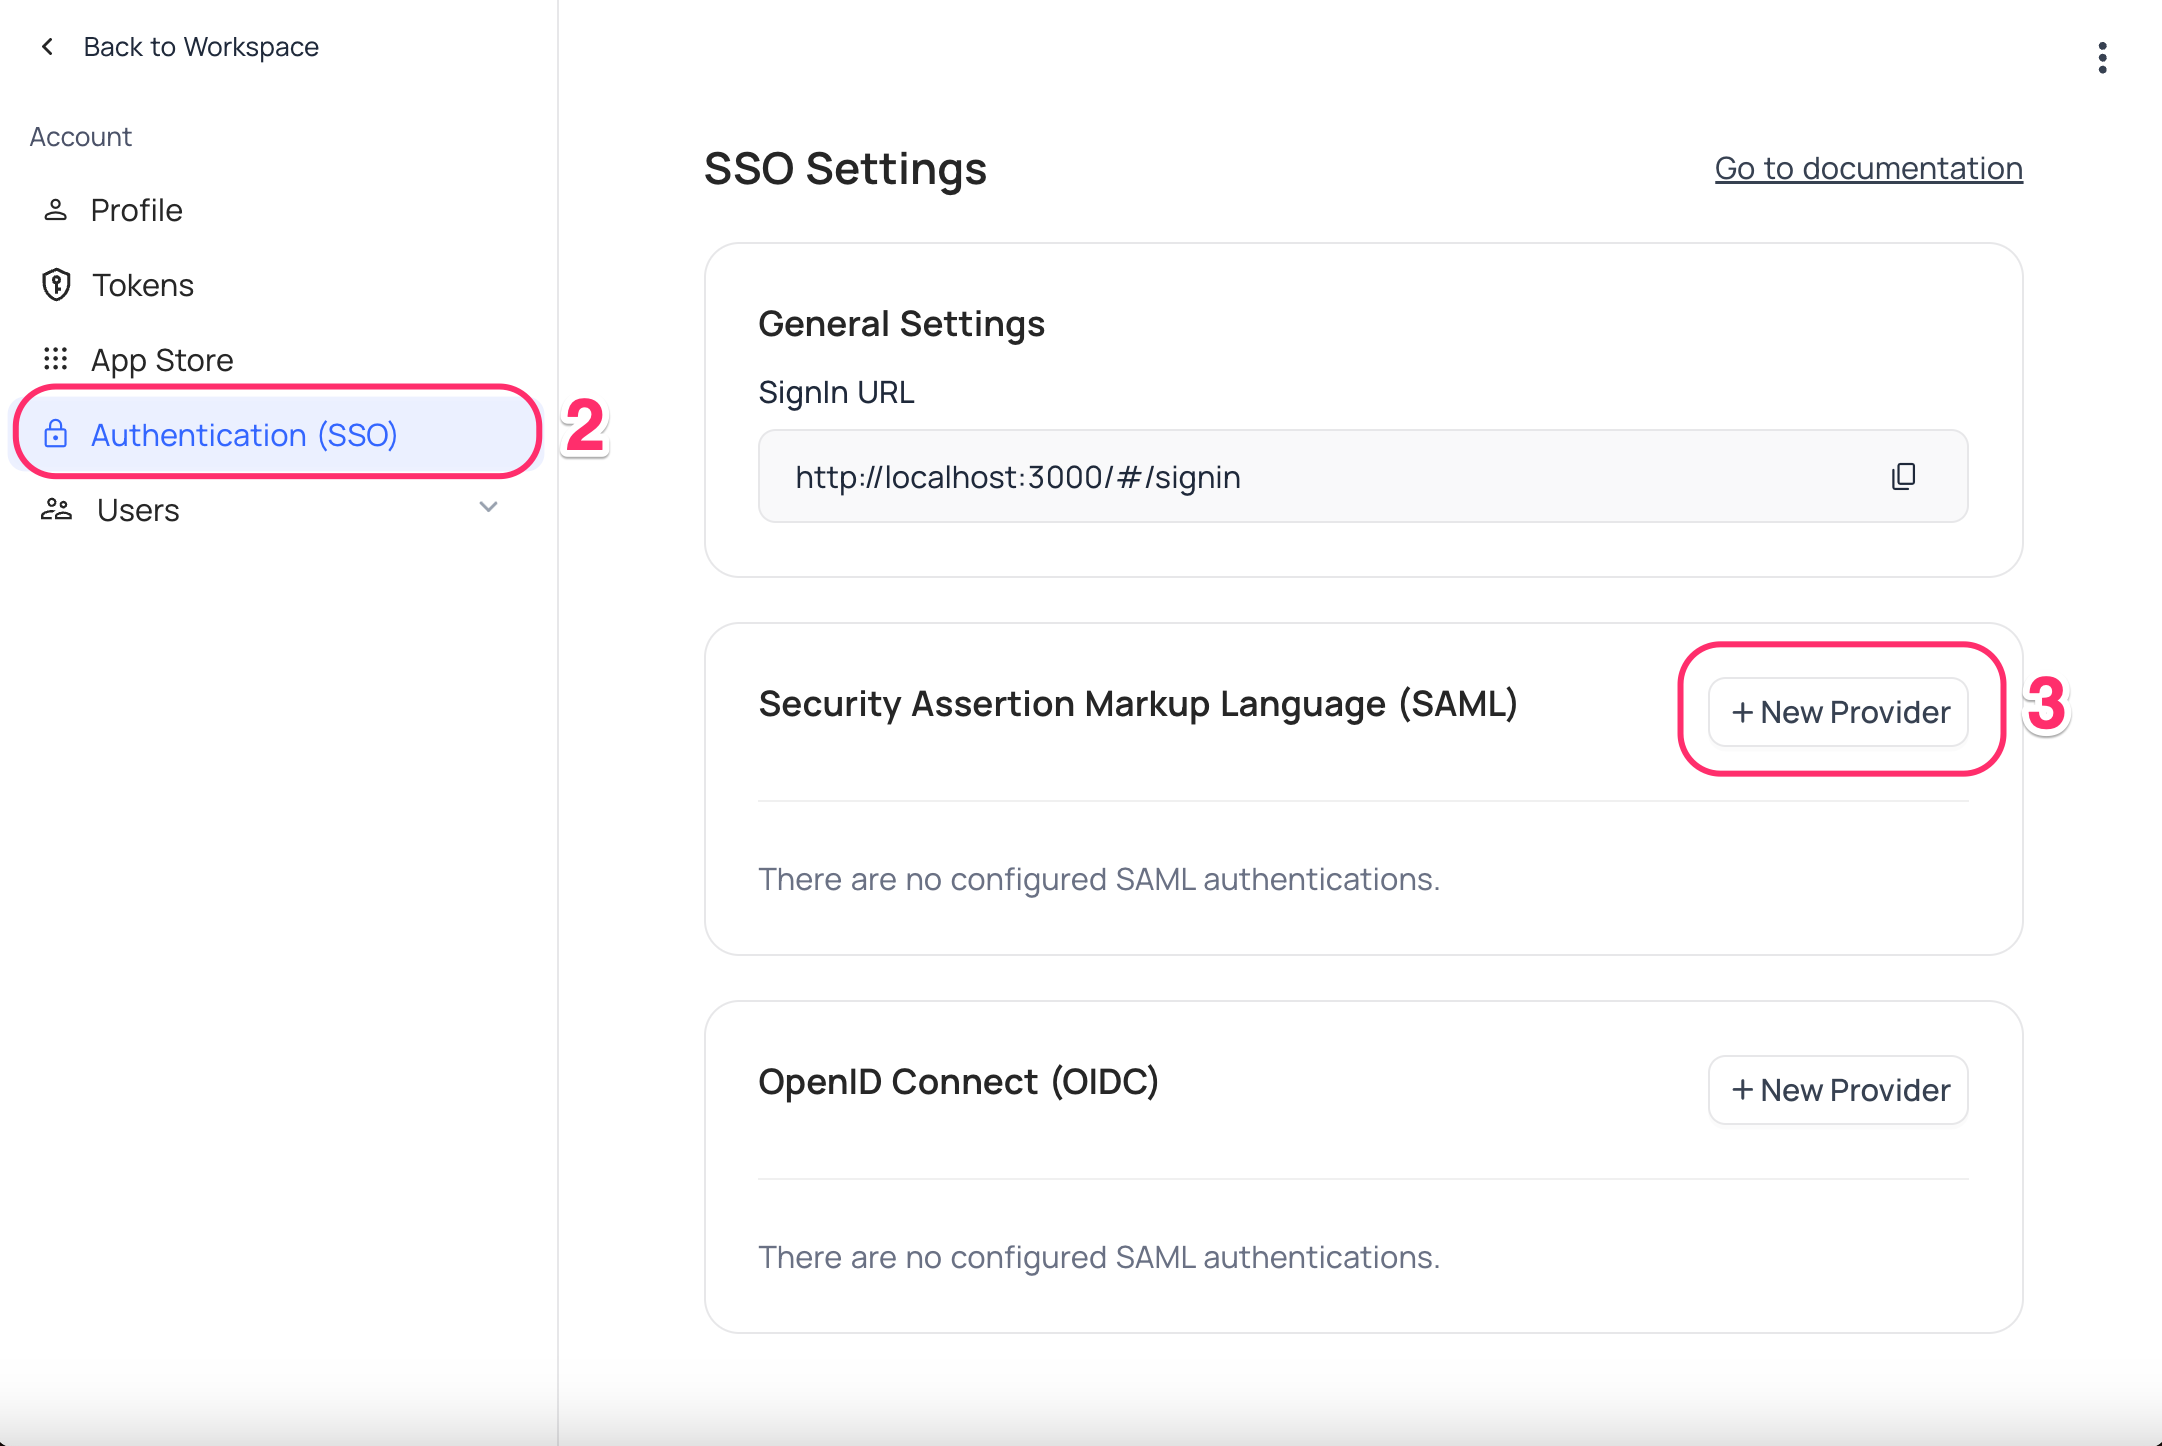
Authentication (SSO) - Click on
New Providerbutton - On the Popup modal, Specify a
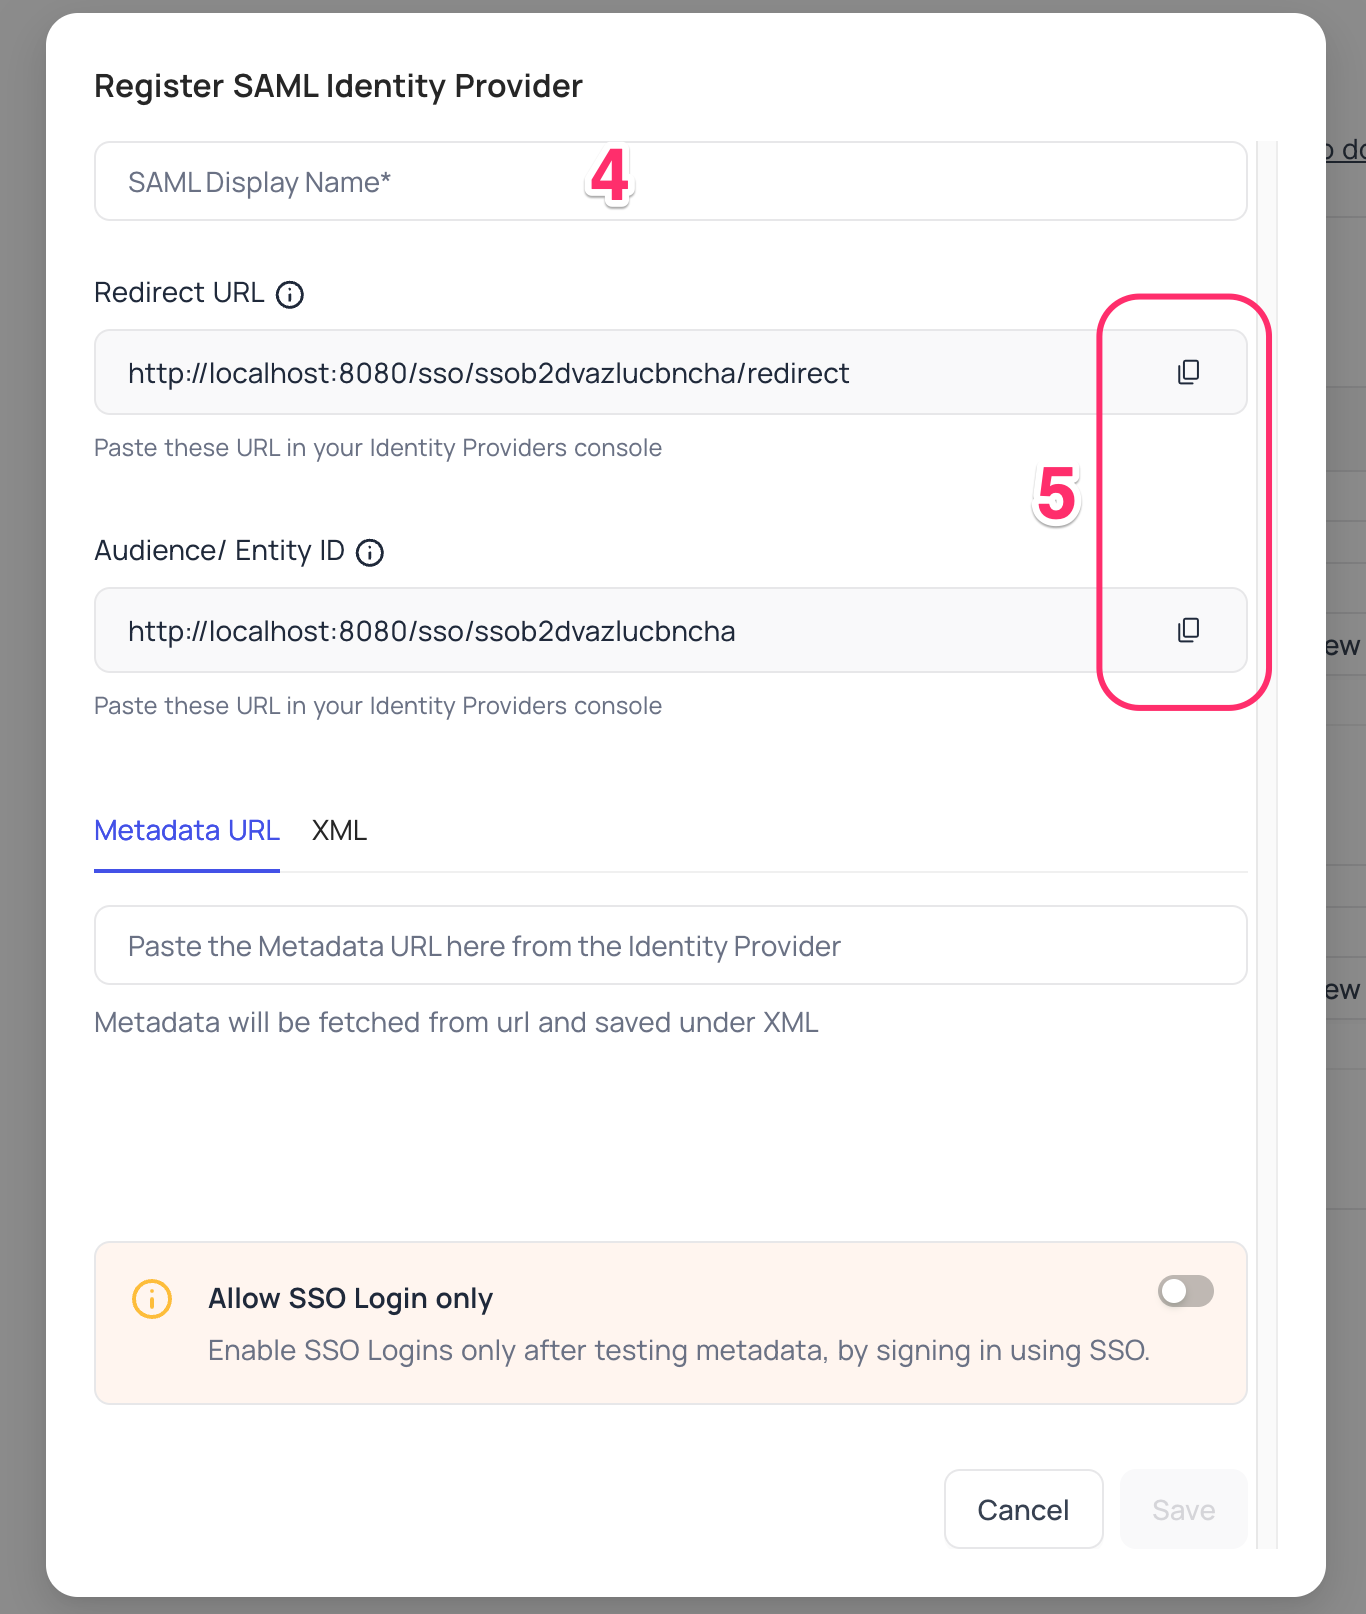
Display namefor the provider; note that, this name will be used to display the provider on the login page - Retrieve
Redirect URL&Audience / Entity ID; these information will be required to be configured later with the Identity Provider
Auth0, Configure NocoDB as an Application
Access your Auth0 account
- navigate to
Applications>Create Application.
- navigate to
In the
Create Applicationmodal,- choose
Regular Web Application - click
Create
- choose
Upon successful creation, you will be directed to the
Quick Startscreen.- Go to the
Addonstab. - Enable
SAML2 Web App
- Go to the
On the
SAML2 Web Appmodal,- Paste
Redirect URLcopied in step above intoApplication Callback URLfield - In Settings, retain
nameIdentifierProbesas["http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress"]; remove other probes if any
{ "nameIdentifierProbes": [ "http://schemas.xmlsoap.org/ws/2005/05/identity/claims/emailaddress" ] }- Click
Enableto save the settings
- Paste
On the
Settingstab,- move to
Advanced Settings>Endpoints>SAMLsection, - copy the SAML
Metadata URL
- move to
NocoDB, Configure Auth0 as an Identity Provider
- Go to
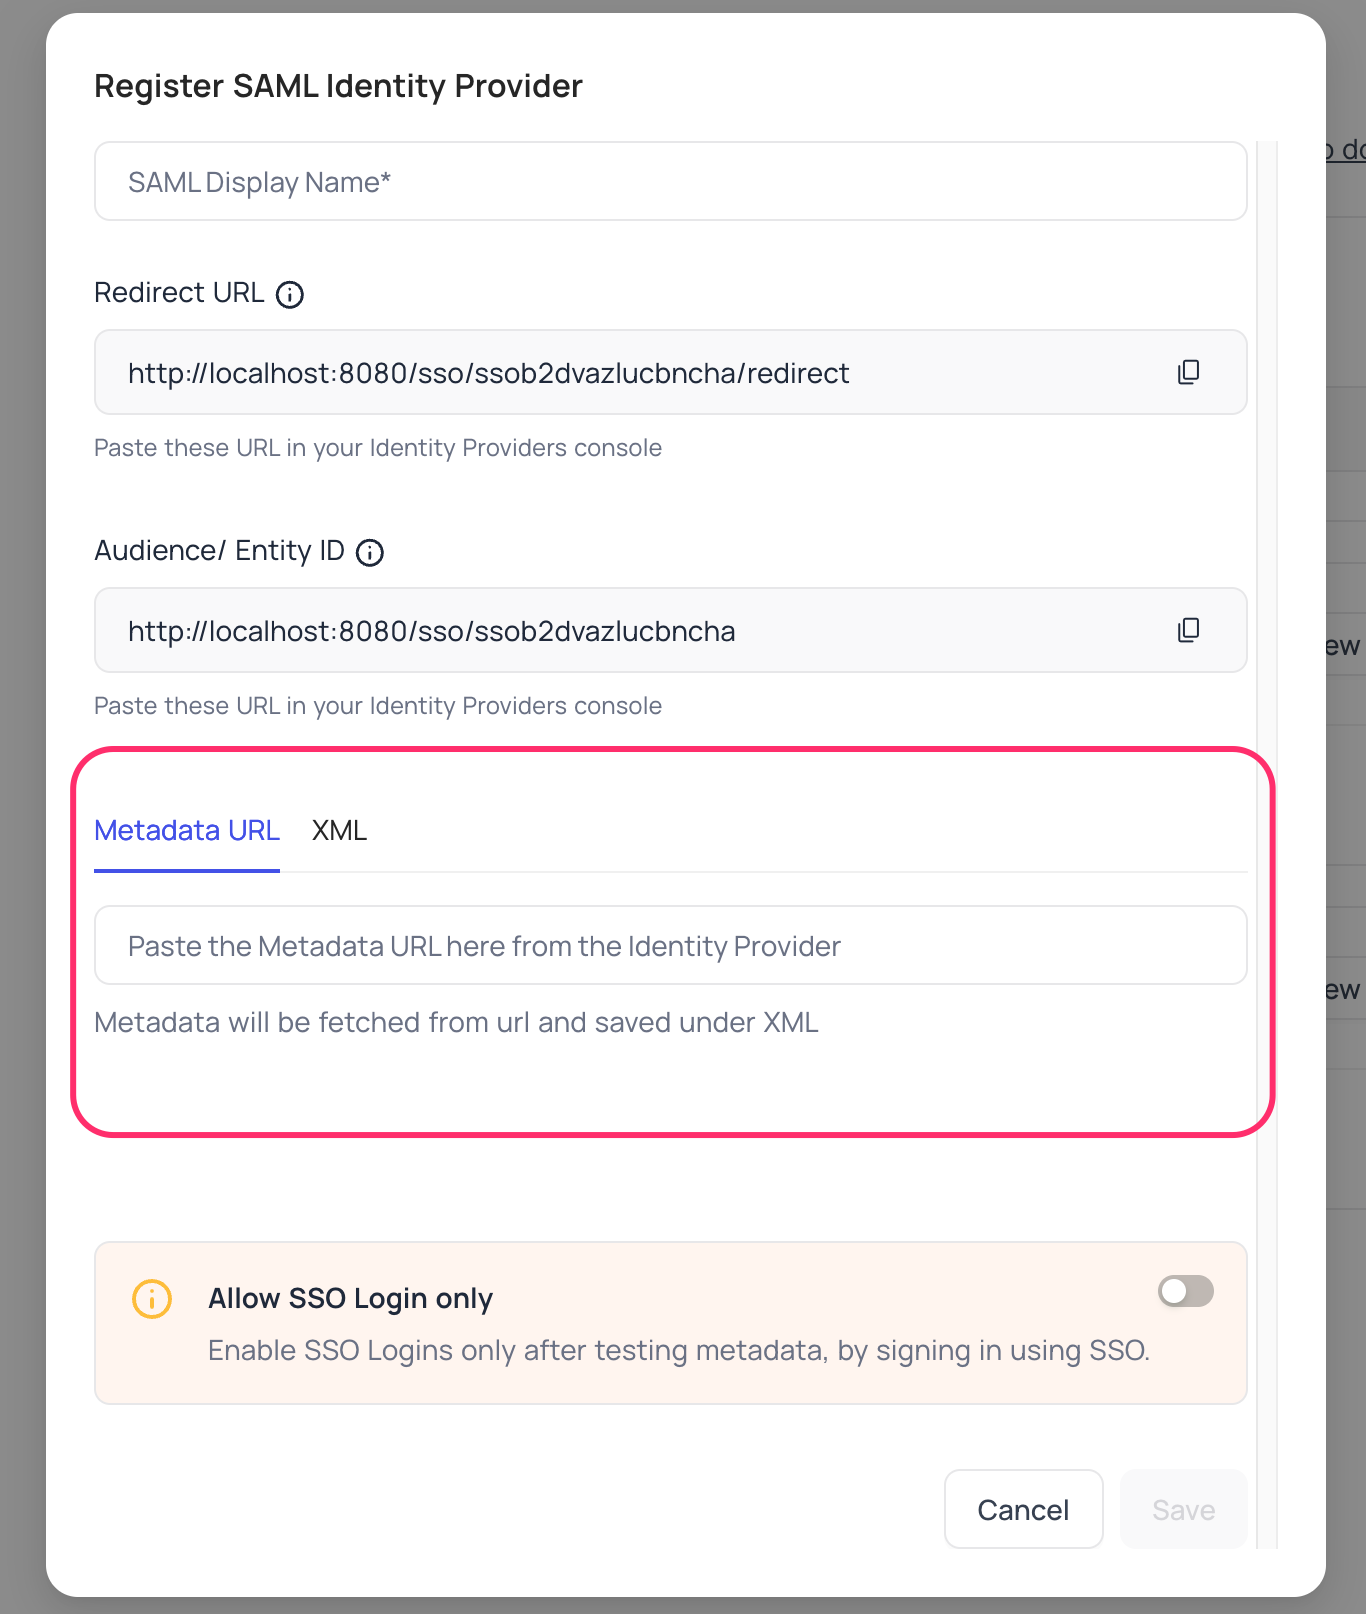
Account Settings>Authentication>SAML - Insert
Metadata URLretrieved in step above; alternatively you can configure XML directly as well Save
For Sign-in's, user should be able to now see Sign in with option.
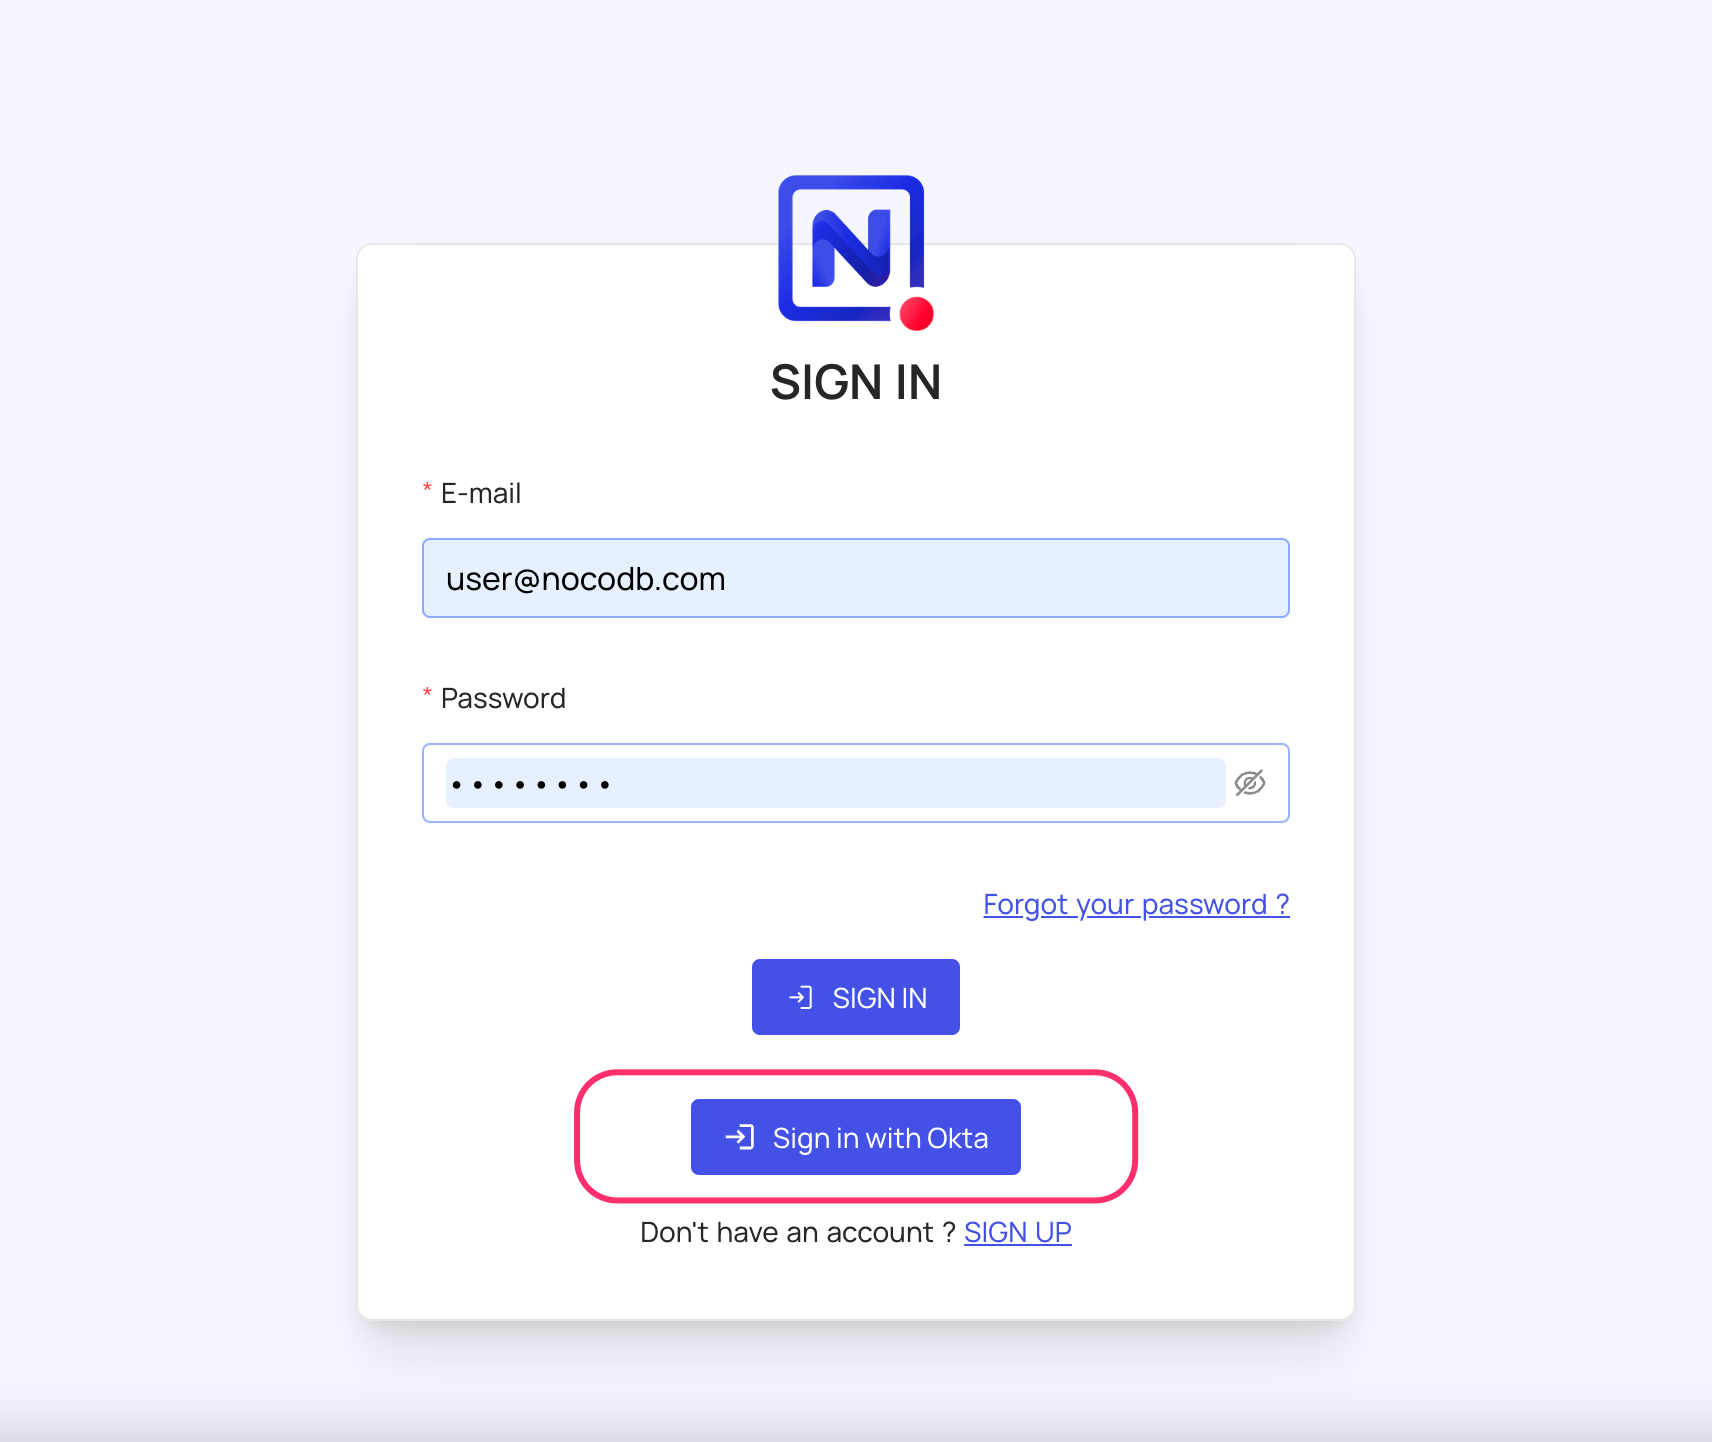
หมายเหตุ: Post sign-out, refresh page (for the first time) if you do not see
Sign in with SSOoption
หมายเหตุ: For more common questions and troubleshooting, see our SSO FAQ .
Availability
- SAML SSO is available on NocoDB Cloud (Business plan and above) and licensed self-hosted deployments (Business plan and above). For access, please reach out to sales team .
- For users on Business plan , the SSO configuration menu is available under Settings > Single Sign-On (SSO) in the workspace sidebar. Refer here for more details.
- Domain Verification Required for Cloud Plans : Before configuring SAML SSO, you must verify your domain in NocoDB (required for both Business and Enterprise plans in the cloud). Only users with email addresses from verified domains can sign in via SSO. See Domain Verification for details.
Related pages
- Okta : Learn how to configure Okta as an identity provider for NocoDB.
- Ping Identity : Learn how to configure Ping Identity as an identity provider for NocoDB.
- Azure AD (Entra) : Learn how to configure Active Directory as an identity provider for NocoDB.
